Cryptographic key governance is the set of policies, processes, and controls that ensures the protection, management, and secure use of the keys used in data encryption.
For financial institutions and companies that operate critical systems, it is essential for meeting regulatory requirements, reducing security risks, and ensuring business continuity.
Why is cryptographic key governance so important?
Digital transformation has significantly increased the volume of sensitive information exchanged between financial institutions, fintech companies, acquirers, credit unions, and payment service providers.
Transactions via Pix, as well as communications with the Central Bank (BACEN), NÚCLEA, and SPED e-Financeira systems, use cryptographic mechanisms to ensure the authenticity, confidentiality, and integrity of the data.
However, all of this security depends on an element that is often overlooked: cryptographic keys.
Even robust encryption algorithms cease to be effective when keys are stored improperly, shared without oversight, or used without clear management policies.
As a result, cryptographic key governance has become one of the pillars of information security in regulated environments.
Cryptographic Key Governance and Management: What's the Difference?
Although the terms are often used interchangeably, they represent distinct and complementary concepts.
Cryptographic key governance is strategic in nature. It establishes the policies, responsibilities, and controls that guide the entire process of protecting the organization's cryptographic assets.
Key management, on the other hand , involves the operational implementation of these guidelines, managing the lifecycle of keys and ensuring that the defined policies are effectively enforced.
In practical terms:
Key Governance
Define:
- Security policies;
- Rules for using the keys;
- Team responsibilities;
- Audit requirements;
- Regulatory compliance;
- Criteria for risk management.
Key Management
Execute:
- Key generation;
- Secure storage;
- Distribution to authorized users;
- Periodic rotation;
- Repeal;
- Audit;
- Usage monitoring.
Effective governance depends on equally robust management. Without proper operational processes, policies fail to produce concrete results.
What are crypto assets?
Governance goes far beyond cryptographic keys.
It encompasses the entire set of assets used to protect systems, users, and digital transactions.
Among them are:
- Cryptographic keys;
- Digital certificates;
- Authentication tokens;
- API credentials;
- Technical terms;
- Credentials used by applications and databases.
All of these assets must be protected throughout their entire lifecycle, as any compromise could lead to unauthorized access, service interruptions, financial fraud, and security incidents.
How does the lifecycle of cryptographic keys work?
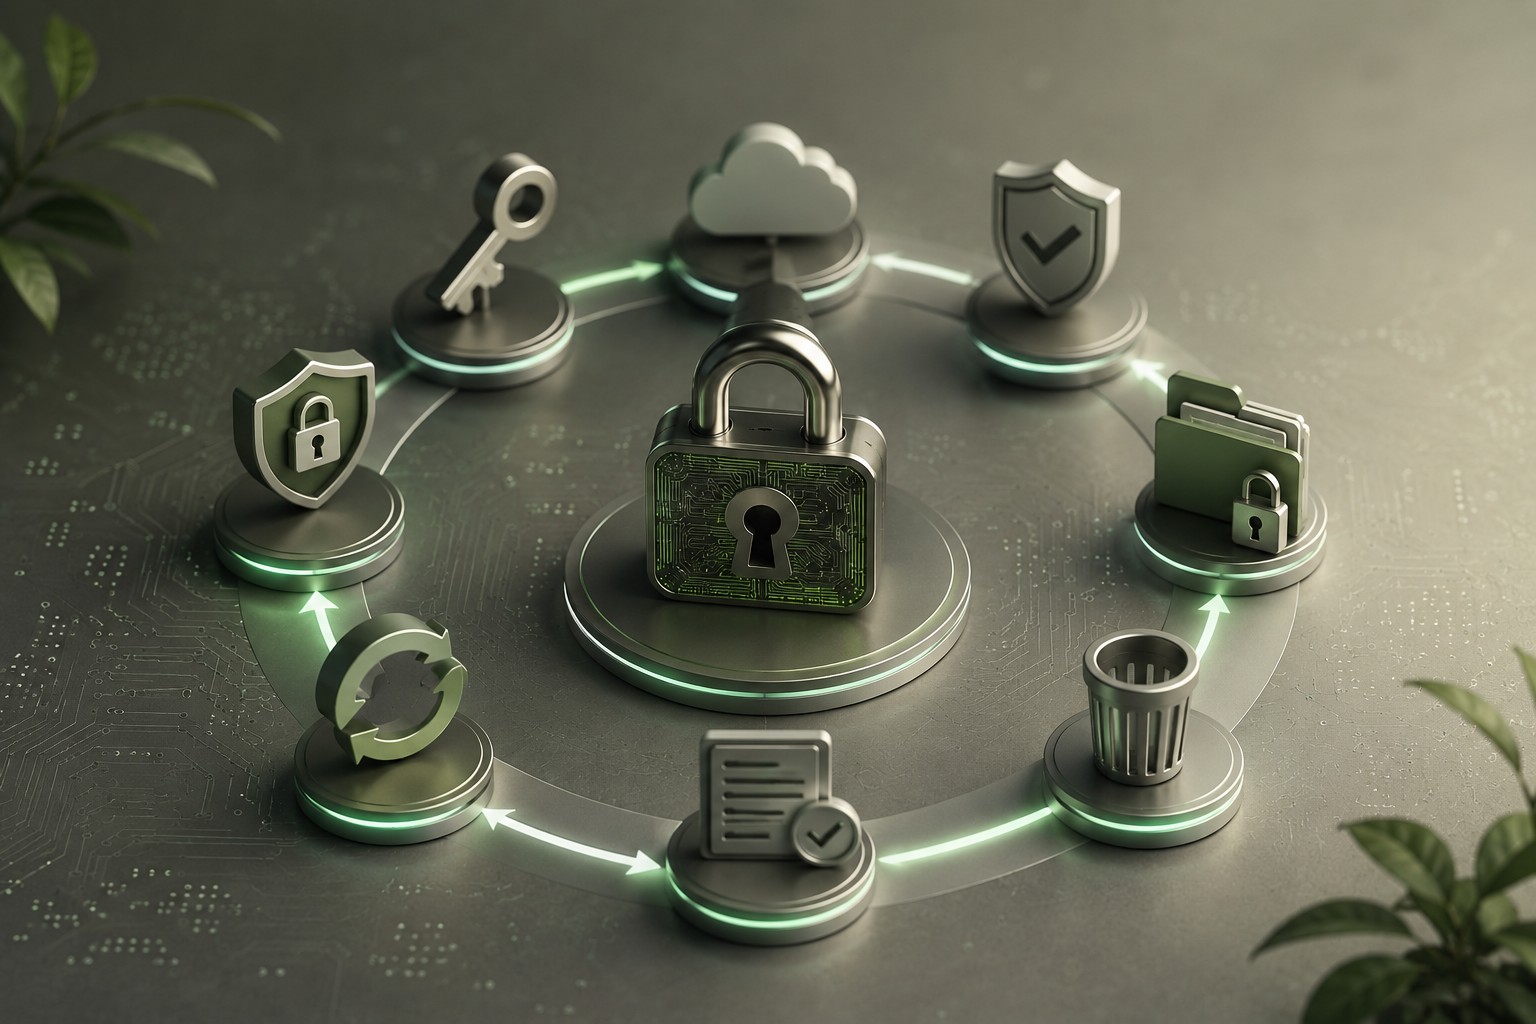
An effective governance strategy covers every stage of the key lifecycle.
Generation
Keys must be generated using secure algorithms and reliable sources of random numbers.
Custody
After they are created, they must be stored in secure environments, such as vaults, HSMs, or specialized key management solutions.
Distribution
Access should be limited to authorized applications and users, using secure channels and robust authentication mechanisms.
Usage
Every cryptographic operation must comply with policies regarding access control, segregation of duties, and traceability.
Rotation
Regular replacement reduces exposure in the event that a key is compromised and meets the requirements of various security standards.
Revocation and Disposal
When keys are no longer in use or are suspected of being compromised, they must be revoked and securely destroyed.
Automating these steps reduces operational risks and facilitates compliance with regulatory requirements.
What are the main challenges of key governance?
The growth of hybrid and multicloud environments has significantly increased the complexity of managing cryptographic assets.
Today, a single organization may have thousands of certificates, credentials, and keys distributed across applications, APIs, microservices, and different infrastructure providers.
Among the main challenges are:
- Maintain an up-to-date inventory of crypto assets;
- Control access permissions;
- Automate the rotation of the keys;
- Ensure the traceability of operations;
- Integrate different custody technologies;
- Comply with financial market regulatory requirements;
- Reduce the risk of downtime caused by expired certificates or compromised keys.
Without structured governance, these challenges significantly increase operational risks.
Best Practices for Strengthening Cryptographic Key Governance
The adoption of appropriate technologies must be accompanied by well-defined processes.
Some of the key best practices include:
- Centralize the management of crypto assets;
- Implement least-privilege policies;
- Use strong authentication for administrative access;
- Automate the generation, distribution, and rotation of keys;
- Maintain a complete audit trail for all operations;
- Use HSMs or Vaults when the level of criticality warrants it;
- Integrate security policies into development processes (DevSecOps);
- Periodically review access policies and asset inventories.
These practices enhance security, reduce human error, and facilitate internal and external audits.
How PRODIST STS Strengthens Cryptographic Key Governance
PRODIST STS was developed to serve financial institutions that need to protect crypto assets and operate with high availability.
The platform combines encryption, digital signature, and centralized key management capabilities into a solution designed for mission-critical environments.
Among its key features are:
Centralized Management of Crypto Assets
The solution enables the management of the entire lifecycle of cryptographic keys, reducing operational complexity and increasing control over assets.
Integration with various custody technologies
The solution supports different key storage models:
- PRODIST's own KMS;
- Integration with certified HSMs;
- Corporate vaults;
- Cloud-based key management services.
This flexibility allows each organization to use the architecture that best suits its security policies.
Security for Critical Environments
The platform offers:
- Certificate-based authentication (mTLS);
- Role-Based Access Control (RBAC);
- Audit of operations;
- Integration via components, file systems, or microservices using OAuth2;
- On-premises, hybrid, or cloud deployment.
In addition, PRODIST STS meets the technical requirements of various systems operated by BACEN, NÚCLEA, Pix, and SPED e-Financeira, enabling financial institutions to strengthen their security without significantly altering their existing architecture.
Count on PRODIST to strengthen cryptographic key governance
Since 1987, PRODIST Technologies has been developing encryption and digital security solutions tailored to the Brazilian financial market.
Its technology has been used in critical operations since the implementation of the Brazilian Payment System (SPB), supporting banks, fintech companies, credit unions, acquirers, sub-acquirers, and software companies that need to combine security, performance, and regulatory compliance.
In addition to software development, PRODIST serves as a strategic partner in the implementation, integration, and support of critical environments, helping organizations protect cryptographic assets and reduce operational risks.
If your organization is looking for a robust solution to strengthen cryptographic key governance, meet regulatory requirements, and enhance the security of your operations, the PRODIST team is ready to support your project!
FAQ – Cryptographic Key Governance
It is the set of policies, processes, and controls that defines how cryptographic keys should be created, protected, used, audited, and discarded to ensure information security.
Governance establishes rules, responsibilities, and policies. Management implements these guidelines by managing the key lifecycle through processes and technologies.
Because it protects crypto assets, reduces the risk of fraud, ensures the traceability of transactions, and helps ensure compliance with financial market regulatory requirements.
PCS offers centralized key management, integration with HSMs, Vaults, and cloud-based KMS, mTLS authentication, access control (RBAC), auditing, and support for the main systems of BACEN, NÚCLEA, Pix, and SPED e-Financeira.
Yes. PRODIST STS supports on-premises, hybrid, and cloud architectures, integrating with the organization's security policies and existing infrastructure.